
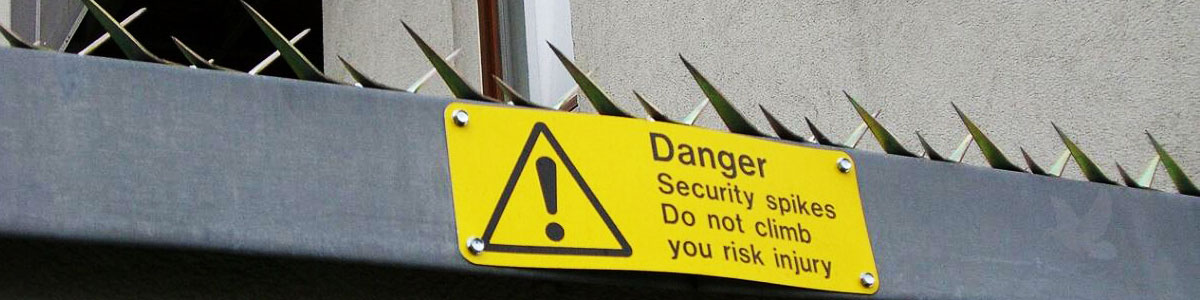
Security Begins Before the Door
A Difficult Target Can Be Less Attractive Than an Easy One
Physical security is not limited to stopping someone after an intrusion has already begun. An important part of protection is making unauthorized access difficult, visible, time-consuming, and risky enough that the location becomes a less appealing target in the first place.
Barriers, controlled entrances, locks, lighting, warning signs, surveillance, and restricted areas can all contribute to that objective. No individual measure guarantees protection. The strength comes from combining measures so that bypassing one does not provide unrestricted access to everything behind it.
Deterrence Has Value Before Contact Occurs
A visible security measure can influence behavior without ever being physically tested. If a potential intruder recognizes that entry will be difficult or likely to be detected, the protection has already performed part of its job.
Physical Protection Can Be Viewed as Prevention, Detection, and Recovery
The original article divides physical security into three broad responsibilities: preventing an incident where possible, detecting what happens when protection is breached, and recovering after theft, damage, or disaster.
These functions complement one another. Prevention attempts to stop unauthorized access. Detection establishes awareness and evidence when something happens. Recovery addresses the consequences and helps restore normal operation.
Prevention
Barriers, locks, controlled entrances, guards, restricted areas, and other measures make unauthorized physical access more difficult.
Detection
Cameras, alarms, access records, monitoring, and other controls help establish that an event occurred and provide information about it.
Recovery
Backups, continuity plans, replacement procedures, documentation, and tested recovery processes help restore operations after an incident.
Visible Protection Can Change the Decision to Attempt Entry
The anti-climb spikes shown in the article image are a straightforward example of deterrence combined with prevention. The physical obstacle makes climbing more difficult, while the warning sign communicates that the barrier exists and that attempting to cross it carries a risk of injury.
Security cameras, guards, alarms, controlled gates, lighting, and access restrictions can create a similar effect. Their purpose is not merely to react to a crime. Their visibility can signal that the location is protected and that unauthorized activity may be noticed.
The easiest incident to recover from is one that deterrence prevented from happening in the first place.
Perimeter Security Creates Distance Between the Public and Protected Assets
A useful physical-security design does not necessarily begin at the server room or equipment cabinet. Protection can start at the property boundary, parking area, exterior entrance, lobby, elevator, hallway, or another point well before someone reaches sensitive hardware.
Each controlled boundary creates another decision point. A person who legitimately needs access can proceed through the appropriate authorization process, while someone without permission encounters increasing resistance as the protected area becomes more sensitive.
Distance Can Become Part of the Defense
The more controlled boundaries that separate an unrestricted area from critical equipment, the fewer opportunities an unauthorized person has to reach that equipment without being challenged or detected.
Not Everyone Inside a Building Needs Access to Every Area
Physical access can be divided according to responsibility. A visitor may need access to a reception area. Employees may require access to normal workspaces. Technical personnel may need additional authorization for server rooms, network closets, storage areas, or other locations containing sensitive systems.
The original article identifies locks, badges, passcodes, and controlled elevator access among the methods that can restrict entry. These controls become more useful when permissions correspond to an actual business need rather than simply granting broad access to everyone inside the facility.
Why Restrict Access Inside an Already Secure Building?
Passing through the exterior entrance does not establish a need to reach every internal system. Additional access boundaries reduce exposure of critical equipment and limit how far an unauthorized or compromised individual can move.
Physical Security Also Protects Documents and Portable Devices
Servers and network equipment are obvious physical assets, but information can leave a facility through many smaller objects. Laptops, external drives, removable media, printed records, backup devices, access cards, and unattended documents can all contain or provide access to sensitive information.
The original article makes the important distinction that IT personnel may not control an entire building’s physical security while still remaining responsible for protecting systems, documents, and devices within their area of responsibility.
Protect the Information, Not Only the Machine
A locked server room provides little protection for sensitive information that has been copied to an unsecured portable drive, left in printed documents, or stored on an unattended laptop elsewhere.
A Barrier Cannot Explain What Happened After It Was Bypassed
Prevention is important, but physical controls can fail or be defeated. Detection provides the next layer by helping establish when an event occurred, which area was affected, and what activity took place.
The source article identifies surveillance as an important detection method and emphasizes determining what was accessed or taken and how the breach occurred.
Detection Answers Different Questions Than Prevention
A lock attempts to prevent entry. A camera, alarm, access record, or monitoring system can help establish that someone entered, when it happened, and which part of the environment may have been affected.
Surveillance Works Best as Part of a Larger Security System
A camera can record activity, but recording alone does not physically prevent someone from crossing a boundary. Similarly, a strong lock can restrict access without creating a visual record of someone attempting to defeat it.
Combining controls gives each measure a more focused role. Barriers delay or prevent entry, access systems regulate authorized movement, alarms call attention to events, and surveillance can provide information about what occurred.
Different Controls Should Support One Another
Security becomes stronger when one layer compensates for limitations in another. The objective is not to find one perfect device, but to create a system in which multiple protections work together.
Physical Barriers Cannot Protect a Poorly Controlled Network by Themselves
The original article also discusses operational security, including network access control, authentication, security policies, external connections, backups, and everyday network operation.
This provides an important boundary between two forms of protection. Physical security controls who can physically reach equipment and locations. Operational security controls how systems, accounts, networks, and information are used. A secure environment requires both because success in one area does not compensate for serious weakness in the other.
Physical Control
Determines who can physically reach a building, room, cabinet, device, document, or other tangible asset.
Operational Control
Determines how systems and information are accessed, authenticated, connected, administered, backed up, and used during normal operation.
A Security Policy Only Works When the System Actually Enforces It
The source gives an example of a password policy that requires periodic changes but still allows users to reuse the same password immediately. The written requirement exists, but the technical implementation defeats its purpose.
The same principle applies to physical security. A restricted-area sign has limited value if the door is routinely left unlocked. An access badge system is weakened if credentials are casually shared. A surveillance system loses value if nobody notices that recording has stopped.
A Control That Exists Only on Paper Is Not Enough
Policies, signs, procedures, and equipment need to function together in actual daily use. A security measure that is routinely bypassed can create the appearance of protection without providing the intended result.
Physical Security Must Account for Events That Cannot Be Prevented
Theft and deliberate intrusion are not the only physical threats to computer systems. Fire, flooding, severe weather, electrical events, structural damage, and other disasters can make equipment unavailable even when no security boundary was intentionally breached.
The original article asks an important recovery question: if a server room were destroyed, how long would the organization need to resume operation? That shifts physical security from protecting equipment alone to protecting the organization’s ability to continue functioning.
The Asset and the Function Are Not the Same Thing
A destroyed server may be replaceable. The greater problem can be the data, configuration, applications, records, and business processes that depended on it. Recovery planning protects the ability to restore those functions.
Backups Become Part of Physical Security When the Original Location Is Lost
A backup stored beside the equipment it protects can be exposed to the same fire, flood, theft, or physical disaster. Recovery planning therefore has to consider where copies are stored as well as whether they exist.
The source recommends off-site backups, recovery timelines, restore testing, and business continuity documentation. These measures help determine whether important information can actually be restored after the original systems are no longer available.
A Backup Is Most Valuable When It Can Be Restored
Recovery planning should include testing. Discovering after a disaster that a backup is incomplete, inaccessible, or unusable defeats the purpose of maintaining it.
The Goal Is Not to Make a Facility Impossible to Enter
Absolute physical security is rarely realistic. Buildings need entrances. Employees need access. Equipment requires maintenance. Deliveries arrive. Emergency exits must remain usable. The objective is to control legitimate movement while making unauthorized access increasingly difficult and detectable.
That is why physical security works best in layers. A visible deterrent may discourage an attempt. A barrier can slow it down. Access control can stop unauthorized movement. Detection can reveal a breach. Recovery planning can reduce the damage if prevention ultimately fails.
Security Is a Sequence, Not a Single Object
The fence, spikes, lock, badge reader, alarm, camera, backup, and recovery plan perform different jobs. Their value comes from how those jobs combine into a complete protection strategy.
A Less Tempting Target Is Only the Beginning
Making a physical location difficult to approach or enter can reduce its attractiveness as a target, but deterrence is only the first layer. Sensitive areas still need appropriate access controls, important activity needs to be detectable, and critical systems need a recovery path if physical protection fails.
The strongest approach treats prevention, detection, operational controls, and recovery as connected responsibilities. The visible spikes above a wall may be the first thing someone notices, but the security of the systems behind that wall depends on every layer that follows.
